Cetbix Sentinel
One Platform for Asset Intelligence, Software Governance & Cyber Risk
Cetbix supports multi-framework compliance and provides end-to-end traceability across assets, risks, controls, and audit evidence, making it particularly suitable for organizations implementing structured management systems.
Discovery model
Cetbix intelligence depthDiscover every asset. Control every license. Identify relevant vulnerabilities. Understand attacker behavior. Prioritize what matters. Remediate faster.
Cetbix Sentinel is an AI-powered technology intelligence platform that unifies IT/OT/Cloud asset discovery, software asset management, license governance, vulnerability intelligence, CISA KEV monitoring, MITRE ATT&CK context, compliance intelligence, and AI-guided remediation in one centralized solution.
Instead of managing asset inventory, software licensing, vulnerability data, exploitation intelligence, and remediation through disconnected tools, Sentinel connects them into a single intelligence model.
Know what you have. Know what's vulnerable. Know what's being exploited. Know how attackers operate. Know what to fix first.
From Asset Discovery to Cyber Risk Intelligence
From Asset Discovery to Cyber Risk Intelligence
Traditional asset discovery answers one question:
What do we have?
Cetbix Sentinel goes further.
It connects discovered infrastructure with software, licensing, vulnerability, exploitation, and attack intelligence so organizations can understand not only what exists, but also what presents risk and what requires action.
Sentinel creates a continuously enriched relationship between:
Asset → OS → Software → Version → License → CVE → Exploitation → ATT&CK → Risk → Secure Version → Remediation
This gives IT, security, compliance, and management teams a shared intelligence layer for understanding the technology estate.
Cetbix Sentinel Intelligence Depth Overview
One Technology Estate. Multiple Layers of Intelligence.
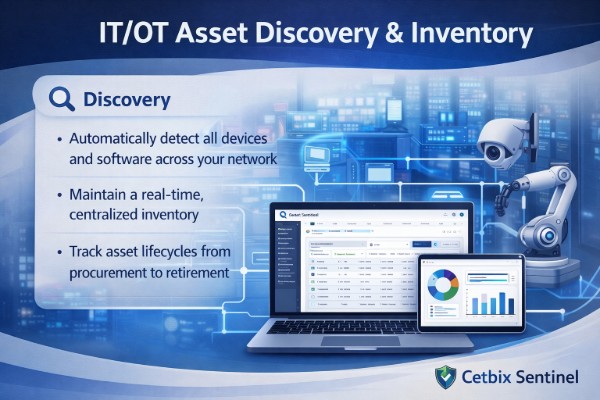
Layer 1 - Asset Intelligence
What do we have?
Continuously discover and inventory technology across IT, OT, cloud, virtual, and connected environments.
Sentinel provides visibility into:
- Hardware and endpoints
- Operating systems
- Virtual machines
- Cloud resources
- Connected infrastructure
- Installed applications
- Software versions
- Unmanaged assets
- Unauthorized assets
- Asset lifecycle information
The result is a centralized technology inventory that establishes the foundation for every other intelligence layer
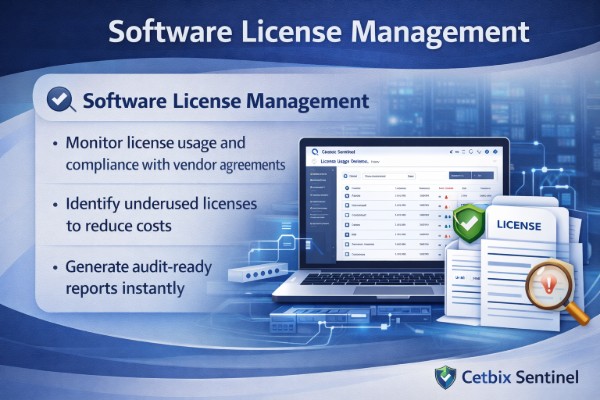
Layer 2 - Software Intelligence
What is running across our environment?
Sentinel maps discovered software and versions to individual assets and infrastructure.
Teams can identify:
- Installed applications
- Application versions
- Software-to-device relationships
- Outdated applications
- Unauthorized software
- Duplicate software
- Software usage
- Application distribution across the organization
Instead of maintaining isolated software lists, organizations gain a continuously updated view of their software estate.
Layer 3 - License Intelligence
Are we properly licensed—and are we spending efficiently?
Sentinel connects software installations and usage with entitlement information.
The platform can monitor:
- License entitlements
- Installed instances
- Software utilization
- Subscription licenses
- Perpetual licenses
- SaaS licensing
- Enterprise agreements
- Renewal dates
- Expiration dates
- Potential over-deployment
- Underutilized licenses
- Unused software
This enables organizations to identify both compliance exposure and software cost optimization opportunities.

Layer 4 - Vulnerability Intelligence
What is vulnerable?
Sentinel correlates discovered software and versions with known vulnerability intelligence.
For relevant software, teams can investigate:
- CVE identifiers
- CVSS scores
- Severity
- Affected products and versions
- Vulnerability descriptions
- Exploitation prerequisites
- Potential impact
- Available remediation
- Recommended secure versions
This changes vulnerability management from reviewing an external universe of CVEs to understanding vulnerabilities in the context of the organization's actual technology stack.
Layer 5 - Exploitation Intelligence
What is actually being exploited?
Severity alone does not tell security teams what attackers are targeting.
Sentinel integrates CISA Known Exploited Vulnerabilities (KEV) and exploitation intelligence to highlight vulnerabilities with evidence of real-world exploitation.
Teams can monitor:
- Known exploited CVEs
- CISA KEV status
- Date added to KEV
- Required remediation dates
- Ransomware associations
- Recently exploited vulnerabilities
- Affected vendors
- Affected products
- Newly emerging exploitation activity
Most importantly, Sentinel can distinguish between:
All Known Exploited Vulnerabilities
and
Known Exploited Vulnerabilities Affecting Our Stack
That distinction helps turn a global vulnerability feed into organization-specific security intelligence.
Layer 6 - Attack Intelligence
How could attackers use the weakness?
Sentinel enriches vulnerability information with MITRE ATT&CK context to help teams understand how vulnerabilities and compromised technologies may relate to attacker behavior.
Where relevant intelligence is available, teams can connect technical risk with:
- ATT&CK tactics
- ATT&CK techniques
- Initial-access patterns
- Execution behavior
- Privilege escalation
- Credential access
- Persistence
- Lateral movement
- Defense evasion
- Potential attacker objectives
This gives defenders more context than a CVE and severity score alone.
The question changes from:
“How severe is this vulnerability?”
to:
“How could this vulnerability matter in an actual attack against our environment?”
Cetbix Sentinel Software Intelligence Overview
License Intelligence: Software Usage & Behavior Intelligence
Layer 7 - Risk Intelligence
What should we fix first?
A Critical CVSS score does not automatically mean a vulnerability represents the greatest risk to every organization.
Cetbix Sentinel combines multiple signals to help prioritize remediation:
- CVSS severity
- CISA KEV status
- Evidence of active exploitation
- Ransomware association
- Installed software version
- Presence within the organization's environment
- Number of affected assets
- Exposure
- Exploitation prerequisites
- ATT&CK context
- Available patches or upgrades
- Recommended secure versions
- Operational and business context
This enables organizations to prioritize vulnerabilities based on relevance and practical exposure, not severity alone.
Layer 8 - AI Remediation Intelligence
What should we do about it?
Finding vulnerabilities is only useful when teams can act on them.
Cetbix Sentinel's AI Software Advisory and remediation capabilities transform vulnerability intelligence into practical guidance.
For affected software, Sentinel can provide:
- Installed version
- Recommended secure version
- CVE
- CVSS score
- Risk assessment
- Impact analysis
- Exploitation context
- Upgrade recommendation
- Remediation guidance
- Structured action plan
The objective is to move teams from:
Alert → Investigation → Decision → Remediation → Verification
without forcing administrators to manually assemble context from multiple disconnected sources.
Layer 9 - Software Usage & Behavior Intelligence
What is being used, how is it used, and what stands out?
Cetbix Sentinel enriches software inventory with available usage and process information to help organizations understand application activity across their technology estate.
By connecting software, processes, devices, and available usage data, Sentinel helps teams identify patterns that may indicate inefficiency, policy violations, unnecessary software expenditure, or potential security concerns.
Teams can investigate:
- Application and process activity across discovered assets
- Software that appears unused or underutilized, where usage data is available
- Applications running on unexpected devices
- Unapproved or unauthorized software activity
- Duplicate or functionally overlapping applications
- Unusual software distribution across endpoints
- Potentially unnecessary software installations
- Applications that warrant further security investigation
This layer helps distinguish between software that is installed, software that is being used, and software that may require attention.
The result is better-informed software governance, more effective license optimization, and additional context for security and compliance decisions.
Note: Usage insights depend on the telemetry and collection capabilities available in the environment; process presence alone does not establish actual user activity or malicious behavior.
Cetbix Sentinel AI-Guided Remediation
From Detection to Verified Resolution
Sentinel can generate a structured remediation workflow based on the vulnerability and affected software.
1. Inventory
Identify every affected installation and asset.
2. Validate
Confirm the installed version, vulnerability conditions, exposure, and relevant vendor security guidance.
3. Assess
Evaluate CVSS severity, exploitation intelligence, KEV status, ransomware associations, attack context, and organizational relevance.
4. Recommend
Identify an appropriate secure software version or remediation path.
5. Test
Validate updates on representative systems before broader deployment.
6. Deploy
Use approved endpoint-management, software-deployment, or operational processes to implement remediation.
7. Verify
Rescan the environment and confirm vulnerable versions have been upgraded, removed, or otherwise remediated.
8. Investigate
Where exploitation is known or suspected, review endpoint, application, identity, and security telemetry for signs of compromise.
Detect → Prioritize → Remediate → Verify
Sentinel helps turn vulnerability intelligence into an operational process.
Core Sentinel Capabilities
🔍 IT/OT/Cloud Asset Discovery
Continuously discover technology across the enterprise and maintain a centralized inventory of hardware, software, virtual systems, cloud resources, and connected infrastructure.
Discover what exists—even when it isn't already documented.
💻 Software Intelligence
Map applications, versions, and software activity to assets so teams understand what is installed and where.
Know exactly what software is running across your technology estate.
📄 Software License Management
Track entitlements, installations, usage, renewals, expiration dates, and compliance positions.
Identify unused licenses, underutilized applications, potential over-deployment, and optimization opportunities.
Control licensing while reducing unnecessary software spend.
🛡️ Vulnerability Intelligence
Correlate installed software and versions with CVEs, CVSS severity, affected products, exploitation conditions, and remediation information.
Find vulnerabilities that are relevant to your environment.
🚨 CISA KEV & Exploitation Intelligence
Monitor vulnerabilities known to be exploited in the wild and identify those affecting software actually present in your infrastructure.
Know what attackers are already exploiting.
⚔️ MITRE ATT&CK Intelligence
Connect relevant security findings with attacker tactics and techniques to provide additional context around how weaknesses may contribute to real-world attack paths.
Understand vulnerability risk through the lens of attacker behavior.
🎯 Risk-Based Prioritization
Combine technical severity with exploitation, environmental relevance, exposure, ransomware intelligence, affected assets, and remediation availability.
Fix what matters first.
🤖 AI Software Advisory
Use AI-assisted analysis to explain vulnerability impact, evaluate affected software, recommend secure versions, and generate remediation guidance.
Turn technical findings into understandable actions.
🔧 AI-Guided Remediation
Generate structured remediation plans covering validation, testing, deployment, verification, and follow-up investigation.
Move from detection to action faster.
⚖️ Compliance & Governance
Maintain evidence across assets, software, licensing, vulnerabilities, and remediation activities.
Support:
-
Software governance
-
License compliance
-
Endpoint compliance
-
Vulnerability governance
-
Audit preparation
-
Policy enforcement
-
Remediation tracking
-
Technology risk reporting
Create a defensible record of what was discovered, identified, and remediated.
📊 Analytics & Executive Intelligence
Provide operational and executive dashboards covering:
-
Asset inventory
-
Software distribution
-
License utilization
-
License renewals
-
Compliance
-
Vulnerability exposure
-
CVE severity
-
Exploited vulnerabilities
-
CISA KEV exposure
-
Ransomware-linked vulnerabilities
-
Affected vendors
-
Infrastructure-specific risk
-
Remediation progress
-
Outstanding risk
Technical teams can investigate individual findings while leadership gains a consolidated view of organizational technology risk.
One Intelligence Model
The power of Cetbix Sentinel comes from connecting information that would otherwise remain isolated.
Asset
What technology exists?
↓
Operating System
What platform is it running?
↓
Software
What applications are installed?
↓
Version
Which exact versions are present?
↓
License
Is the software properly licensed and efficiently utilized?
↓
CVE
Is that version affected by known vulnerabilities?
↓
Exploitation
Is the vulnerability being exploited in the wild?
↓
CISA KEV
Has it been identified as a Known Exploited Vulnerability?
↓
MITRE ATT&CK
How could the weakness relate to attacker behavior?
↓
Risk
How relevant is it to this organization's environment?
↓
Secure Version
What version or remediation path should be considered?
↓
Remediation
What actions should administrators take?
↓
Verification
Has the vulnerable condition actually been removed?
One Platform. Multiple Teams.
Sentinel creates a common intelligence layer while giving each team the information relevant to its responsibilities.
Instead of separate teams working from separate versions of the technology estate, Sentinel provides a shared source of intelligence.
Sentinel Intelligence Modules
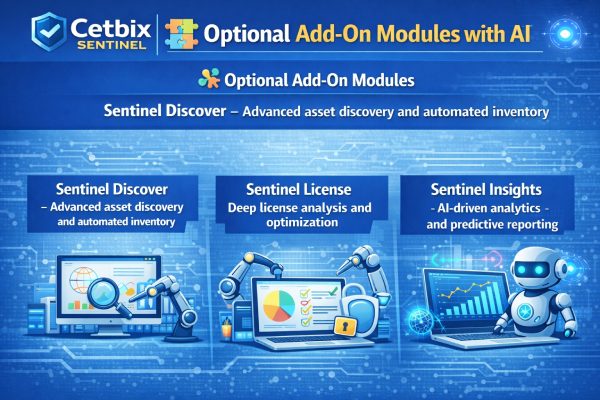
Sentinel Discover
Know what you have.
Asset discovery, endpoint inventory, software discovery, infrastructure visibility, and technology mapping across IT, OT, and cloud environments.
Sentinel License
Know what you own and what you use.
Software entitlement management, utilization, renewals, compliance monitoring, and cost optimization.
Sentinel Vulnerability Intelligence
Know what's vulnerable.
CVE correlation, CVSS analysis, affected-version intelligence, CISA KEV monitoring, ransomware associations, and infrastructure-aware vulnerability analysis.
Sentinel Attack Intelligence
Know how attackers operate.
MITRE ATT&CK context and exploitation intelligence help teams understand vulnerabilities in relation to real-world adversary behavior.
Sentinel AI Advisory
Know what to do next.
AI-powered risk assessments, vulnerability explanations, impact analysis, secure-version recommendations, and structured remediation guidance.
Sentinel Insights
Know where your organization stands.
Executive dashboards, technology-risk analytics, compliance trends, remediation tracking, software optimization, and decision-support intelligence.
Why Cetbix Sentinel?
Know What You Have
Continuously discover IT, OT, cloud, hardware, software, and connected assets.
Know What You're Paying For
Understand software entitlements, utilization, renewals, and optimization opportunities.
Know What's Vulnerable
Map known vulnerabilities to software and versions actually present in your environment.
Know What's Being Exploited
Monitor CISA KEV and other exploitation intelligence to identify vulnerabilities attackers are actively targeting.
Know What Affects You
Filter global vulnerability intelligence against your discovered infrastructure.
Know How Attackers Operate
Use MITRE ATT&CK context to better understand relevant attacker tactics and techniques.
Know What To Fix First
Prioritize remediation using severity, exploitation, exposure, affected assets, ransomware intelligence, and organizational relevance.
Know What To Do Next
Use AI-generated analysis, secure-version recommendations, and remediation guidance to accelerate response.
Know When Risk Is Removed
Rescan affected infrastructure to verify vulnerable software has been upgraded or removed.
From Inventory to Intelligence
Traditional asset management tells you what you own.
Traditional vulnerability feeds tell you what could be vulnerable.
Threat intelligence tells you what attackers are doing.
License management tells you what software you're entitled to use.
Cetbix Sentinel connects these perspectives.
Discover → Govern → Detect → Understand → Prioritize → Remediate → Verify
The result is a continuously enriched view of the organization's technology estate—connecting asset intelligence, software governance, cyber risk, exploitation intelligence, attacker behavior, and remediation.
Turn Technology Data Into Decisions
The modern enterprise does not need another disconnected inventory or another stream of vulnerability alerts.
It needs context.
Which assets do we have?
Which software is installed?
Are we properly licensed?
Which versions are vulnerable?
Which vulnerabilities are being exploited?
Which ones affect us?
How could attackers use them?
What should we fix first?
What version should we deploy?
Have we actually removed the risk?
Cetbix Sentinel brings those answers together.
Know what you have.
Know what's vulnerable.
Know what's being exploited.
Know how attackers operate.
Know what to fix first.
Cetbix Sentinel — From Asset Discovery to Cyber Risk Intelligence.
Feature Comparison
| Capability | Cetbix Sentinel | Microsoft SCCM (MECM) | ServiceNow ITAM | Lansweeper |
|---|---|---|---|---|
| Agentless Discovery | Native & Core Architecture | Primarily Agent-Based | Connector Dependent | Native |
| Deployment Complexity | Low | High | Very High | Moderate |
| Time to Operational Value | Hours | Weeks to Months | Several Months | Days |
| Software Inventory Discovery | Comprehensive | Comprehensive | Comprehensive | Comprehensive |
| License Reconciliation | Built-In Engine | Basic Reporting | Advanced (Complex Configuration) | Limited |
| License Compliance Analysis | Automated | Manual Interpretation | Advanced | Partial |
| Cost Optimization Recommendations | Automatic Insights | Not Native | Available with Configuration | Limited |
| Infrastructure Requirements | Minimal | Extensive | Extensive | Moderate |
| Active Directory Integration | Built-In | Native | Supported | Native |
| Usage Analytics | Included | Limited | Advanced | Basic |
| JSON / API Data Export | Native JSON Export | Limited | Full API Ecosystem | Partial |
| Operational Overhead | Low | High | High | Medium |
| Ease of Use | Simple & Focused | Steep Learning Curve | Enterprise Complexity | Moderate |
| Best Fit | Rapid Asset Discovery, Software Inventory, License Compliance & Cost Optimization | Endpoint Management & Software Deployment | Large Enterprise ITSM / ITAM Programs | General IT Asset Discovery |
1. Built for the Reality of Modern IT
One Connected View Across a Complex Technology Environment
Modern organizations operate across endpoints, servers, cloud platforms, OT systems, and applications—with different teams responsible for different parts of the environment.
Cetbix Sentinel connects these technology layers through a unified intelligence model, helping organizations move beyond fragmented inventories and disconnected security findings.
- Cross-environment visibility — Bring asset and software information together across IT, OT, and cloud.
- Connected intelligence — Link assets and software versions to licensing, vulnerabilities, exploitation intelligence, and remediation.
- Context-driven decisions — Understand which findings are relevant to your actual environment.
- Shared operational understanding — Give IT, security, software asset management, and leadership a common foundation for action.
One technology estate. One connected intelligence layer. Better-informed decisions.
2. From Findings to Measurable Outcomes
Turn Technology Intelligence Into Business Value
Cetbix Sentinel is designed to help organizations make better decisions about technology, software costs, and cyber risk.
Improve Visibility
Reduce blind spots by building a more complete picture of assets, applications, versions, and infrastructure.
Strengthen Security Prioritization
Focus attention on vulnerabilities that affect your environment, especially those associated with known exploitation.
Optimize Software Spending
Identify potential license waste, underutilized entitlements, renewal requirements, and software optimization opportunities.
Support Governance and Compliance
Bring asset, software, license, vulnerability, and remediation information together to support reporting and audit preparation.
Accelerate Remediation
Use AI-assisted analysis and structured recommendations to help teams determine appropriate next steps.
Improve Decision-Making
Give technical teams actionable detail and leadership a clearer view of technology exposure and remediation progress.
The goal is not simply to collect more data. It is to turn technology data into decisions and measurable operational improvements.
3. Your Next Step Toward Connected Intelligence
Stop Managing Technology Risk in Silos
You cannot effectively prioritize what you cannot see. You cannot understand exposure without context. And identifying a vulnerability is only the beginning of remediation.
Cetbix Sentinel connects asset discovery, software intelligence, license governance, vulnerability intelligence, exploitation context, MITRE ATT&CK mapping, and AI-assisted remediation in one platform.
Discover your technology estate. Understand what matters. Make informed decisions. Take action with greater confidence.
Know what you have. Know what's vulnerable. Know what's being exploited. Know what to fix first.
See Cetbix Sentinel in Action
Explore how Sentinel can help your organization connect its technology inventory with software governance and cyber risk intelligence.
Cetbix Sentinel — From Asset Discovery to Cyber Risk Intelligence.