CyFun Compliance Management - NIS 2 Readiness
Cetbix GRC | Cybersecurity Compliance
Simplify CyFun® Compliance with Cetbix GRC
From cybersecurity requirements to measurable cyber resilience.
Manage your CyberFundamentals (CyFun®) implementation through one Governance, Risk and Compliance platform. Bring cybersecurity requirements, risks, controls, evidence and corrective actions together in a structured environment.
Turn compliance activities into clear responsibilities, visible progress and practical security improvements.
Request a Cetbix GRC DemoWhat is CyFun® and why does it matter?
The CyberFundamentals Framework (CyFun®), developed by the Centre for Cybersecurity Belgium (CCB), provides organisations with a structured set of cybersecurity measures to help protect data, reduce exposure to common cyberattacks and improve cyber resilience.
The framework draws on recognised cybersecurity standards and practices, including the NIST Cybersecurity Framework, ISO/IEC 27001 and ISO/IEC 27002, CIS Controls and IEC 62443.
CyFun® 2025 updates the framework to reflect current cybersecurity practices and regulatory developments. The CCB highlights a stronger focus on supply-chain protection and operational technology (OT), clearer controls to support assessment and auditing, and additional governance measures from the IMPORTANT assurance level.
CyFun implementation involves more than completing a checklist. Organisations need to understand applicability, assign control ownership, assess risks, collect evidence, address gaps and monitor progress over time.
Cetbix GRC provides a central environment to organise and manage these activities, helping teams connect compliance work with day-to-day risk management.
Manage your CyFun journey with Cetbix GRC
Cetbix GRC brings governance, risk and compliance activities together so that teams can move away from disconnected spreadsheets, email-based evidence collection and manually maintained registers.
| Capability | How it supports your programme |
|---|---|
| Requirement and control management | Organise applicable requirements, document implementation status and assign accountable owners. |
| Gap assessment | Record assessment results, identify missing or insufficient measures and prioritise areas for improvement. |
| Risk management | Identify, evaluate and prioritise cybersecurity risks and connect them to relevant controls and assets. |
| Evidence management | Centralise policies, procedures, records, technical documentation and management approvals. |
| Corrective action management | Convert identified gaps into actions with owners, priorities, deadlines and follow-up. |
| Audit and assessment preparation | Maintain traceable records and organise documentation for internal reviews and independent assessments. |
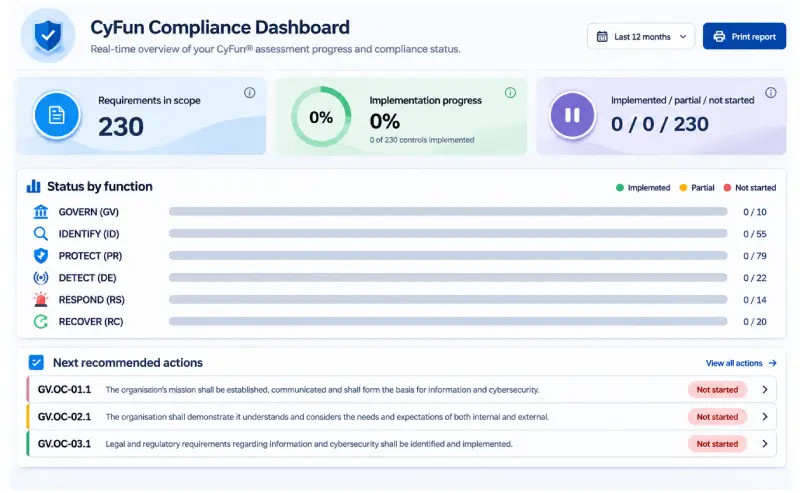
| Dashboards and reporting | Give stakeholders visibility into risks, implementation progress, open findings and overdue actions. |
| AI-assisted workflows | Support analysis and documentation workflows, with review and approval by responsible people. |
One platform. Connected information. Clear accountability. Link risks, controls, assets, evidence and remediation activities to create a more consistent view of your cybersecurity posture.
Structure your programme around the CyFun® assurance levels
CyFun® provides a starting level and three assurance levels. The appropriate level depends on the organisation's context, exposure and applicable obligations. Use the CCB's current guidance and selection tools to determine the level that applies to your organisation.
SMALL
Starting guidance for organisations beginning to structure their cybersecurity approach.
BASIC
A foundational set of cybersecurity measures to address common threats and establish essential practices.
IMPORTANT
A stronger set of measures for organisations with increased risk exposure and security needs.
ESSENTIAL
The most comprehensive assurance level for organisations facing the highest requirements and risk profile.
Cetbix GRC can help organise the activities, owners, evidence and progress associated with the selected scope. The platform does not determine the legally applicable level or replace the CCB's official guidance.
From a CyFun requirement to an accountable action
A useful compliance record connects the requirement being assessed to the risk it addresses, the person responsible, the evidence demonstrating implementation and any corrective action needed.
Illustrative mapping example
Supplier and third-party dependency management
| Framework topic | CyFun® 2025 — supply-chain / supplier dependency security. Confirm the exact requirement identifier and official wording against the CCB catalogue for the selected level. |
|---|---|
| Example risk | RISK-TP-001 — Critical supplier disruption or compromise could affect the confidentiality, integrity or availability of business services. |
| Control owner | Third-Party Risk Manager |
| Accountable role | CISO / Information Security Manager |
| Example evidence | Approved supplier register; supplier risk assessments; relevant contracts and SLAs; assurance reports where available; business continuity and disaster recovery test records; documented critical dependency map. |
| Corrective action | CAPA-TP-001 — Identify critical suppliers, assess their security and resilience, document dependencies and define a periodic review process. Assign an owner and due date. |
| Status | Example status: In progress — evidence and implementation need validation. |
Connect risks, controls, evidence and actions

CyFun® 2025 control library and assessment configuration
CyFun® 2025 includes updated framework materials and self-assessment tools published by the CCB. The Cetbix GRC platform provides the management layer around those materials by structuring requirements, assigning owners, recording assessment results, linking evidence and tracking remediation.
Keep assessment evidence and remediation organised
CETBIX GRC | CYBERSECURITY COMPLIANCE
Simplify CyFun® Compliance with Cetbix GRC
From cybersecurity requirements to measurable cyber resilience.
Manage your CyberFundamentals implementation through one intelligent Governance, Risk and Compliance platform.
What is CyFun®?
The CyberFundamentals Framework (CyFun®), developed by the Centre for Cybersecurity Belgium (CCB), provides organisations with a structured approach to improving cybersecurity and protecting critical information assets.
CyFun helps organisations identify security weaknesses, implement appropriate safeguards and strengthen resilience against cyber threats.
However, implementing CyFun involves more than completing a checklist. Organisations need to manage requirements, risks, responsibilities, evidence, corrective actions and continuous improvement.
Cetbix GRC brings these activities together in one centralised platform.
Manage Your Entire CyFun Journey
One platform to manage cybersecurity governance, risk and compliance.
Control ManagementOrganise CyFun requirements, assign control owners and monitor implementation status. |
Gap AssessmentIdentify missing or insufficient security measures and prioritise improvement opportunities. |
Risk ManagementIdentify, evaluate and prioritise cybersecurity risks and associated business impacts. |
Evidence ManagementCentralise policies, procedures, records and supporting documentation. |
Remediation ManagementAssign corrective actions, responsibilities, priorities and deadlines. |
Reporting & DashboardsMonitor implementation progress, compliance status and outstanding actions. |
From CyFun Requirement to Actionable Compliance
Cetbix GRC provides a structured approach to connecting cybersecurity requirements with risks, controls, owners, evidence and corrective actions.
ILLUSTRATIVE CYFUN 2025 CONTROL MAPPING
GV.OC-05.1 – Supply Chain Dependencies
Identify and document relevant supply-chain dependencies and their impact on organisational operations.
RISK-TP-001: Critical cloud service provider outage or compromise may disrupt business operations.
Inherent risk score: 20/25 (illustrative)
Control owner: Third-Party Risk Manager
Accountable: Chief Information Security Officer (CISO)
- Critical supplier register
- Cloud service contracts and SLAs
- Supplier security assessments
- Business continuity test results
- Supply-chain dependency map
CAPA-TP-001: Establish and maintain an inventory of critical upstream dependencies.
Responsible: Third-Party Risk Manager
Target: 30 days (illustrative)
Status: Open
Monitor implementation, evidence completeness, risk treatment and corrective action closure.
REQUIREMENT → RISK → CONTROL → OWNER → EVIDENCE → ACTION → COMPLIANCE
Make CyFun Compliance Simpler.
Make Cybersecurity Stronger.
Take control of your cybersecurity compliance journey with Cetbix GRC. Bring structure, visibility and accountability to your organisation's cybersecurity programme.
Cetbix GRC | Governance. Risk. Compliance.
CyFun® is a framework developed by the Centre for Cybersecurity Belgium. Cetbix GRC is a compliance management platform and is not itself a CyFun certification or conformity assessment body. All framework references, control mappings and product capabilities must be validated against the applicable official documentation and product configuration.