Complete IT & OT Asset Visibility Without Agents
Agentless IT Discovery, Software Intelligence & License Optimization
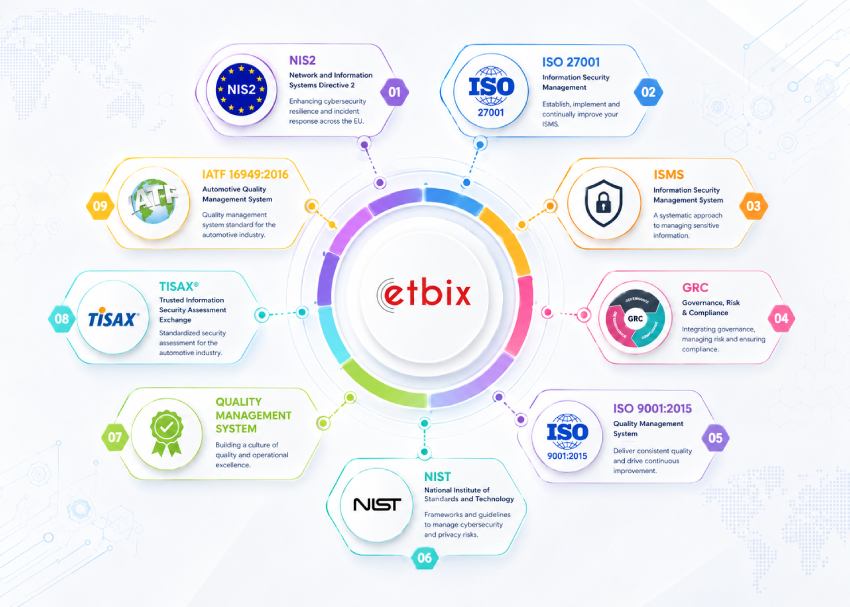
Cetbix supports multi-framework compliance and provides end-to-end traceability across assets, risks, controls, and audit evidence, making it particularly suitable for organizations implementing structured management systems.
Cetbix Sentinel
Agentless Asset Discovery, Software Intelligence, License Governance & Cyber Risk Intelligence
Discover your technology estate. Understand your software. Control your licenses. Identify vulnerabilities. Prioritize risk. Take action.
Cetbix Sentinel is an agentless technology intelligence platform designed to help organizations discover, understand, govern, and secure their IT, OT, and cloud-connected environments.
Sentinel combines asset discovery, hardware and software inventory, software intelligence, usage and behavior insights, license reconciliation, vulnerability intelligence, exploitation intelligence, MITRE ATT&CK context, risk prioritization, and AI-guided remediation within one connected platform.
Instead of managing asset data, software information, licensing, vulnerabilities, and remediation through separate systems, Sentinel connects these datasets to provide deeper operational context.
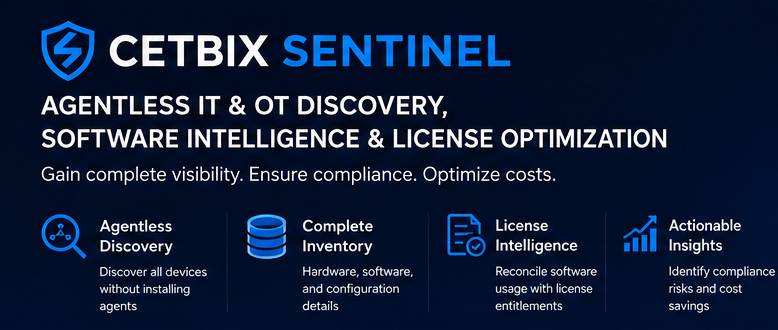
Core Sentinel Capabilities
Seamlessly manage your compliance and information security across multiple cloud environments.
Gap Closure Roadmaps
Identify gaps in your security posture and receive actionable roadmaps to address these deficiencies efficiently.
One Platform. Multiple Layers of Intelligence.
01 — Agentless Asset Discovery
Know what exists across your environment.
Discover network-connected technology without requiring traditional endpoint-agent deployment.
Sentinel helps identify:
- Workstations
- Servers
- Virtual machines
- Network devices
- Infrastructure systems
- OT and industrial technology
- Cloud-connected resources
- Operating systems
- Hardware configurations
- Previously unknown or unmanaged assets
Agentless discovery can reduce deployment complexity while helping organizations establish visibility across environments where installing agents may be difficult or impractical.
Discover first. Understand second. Act with confidence.
Agentless Discovery for Faster Deployment
02 — Hardware Intelligence
Build a Detailed Picture of Every Asset
Asset discovery becomes more valuable when organizations can understand the characteristics of each device.
Cetbix Sentinel can collect and organize hardware information such as:
- Device identification
- Manufacturer
- Model
- Processor information
- Memory configuration
- Storage information
- Network information
- Operating system
- System configuration
- Asset relationships
This information supports IT operations, lifecycle planning, technology assessments, compliance, procurement, and infrastructure management.
From an IP address to an understandable technology asset.
03 — Software Intelligence
Know What Software Is Installed and Where
Software is one of the most important layers of the technology estate.
Sentinel maps discovered applications and software versions to individual assets, helping teams understand what software exists, where it is installed, and how it is distributed.
Organizations can analyze:
- Installed applications
- Application versions
- Software publishers
- Software-to-device relationships
- Running processes
- System services
- Software distribution
- Outdated applications
- Unauthorized software
- Duplicate or overlapping applications
This creates a connected software inventory rather than a collection of disconnected application lists.
Asset → Software → Version
That relationship becomes the foundation for software governance, licensing, vulnerability analysis, and remediation.
Comprehensive Hardware & Software Inventory
Hardware Intelligence
04 — Software Usage & Behavior Intelligence
Go Beyond Software Installation
Knowing that software is installed is only part of the picture.
Where usage and telemetry information is available, Cetbix Sentinel can enrich software inventory with additional context around application and process activity.
Teams can investigate:
- Software that appears unused or underutilized
- Applications running on unexpected systems
- Unapproved software activity
- Duplicate applications
- Unnecessary installations
- Software distribution patterns
- Application and process relationships
- Software requiring further security investigation
This helps organizations distinguish between:
- What is installed.
- What appears to be in use.
- What may require attention.
Usage insights depend on the telemetry and collection capabilities available in the environment; process presence alone does not establish actual user activity or malicious behavior.
Software Intelligence
05 — Software License Intelligence
Connect Software Inventory With Licensing
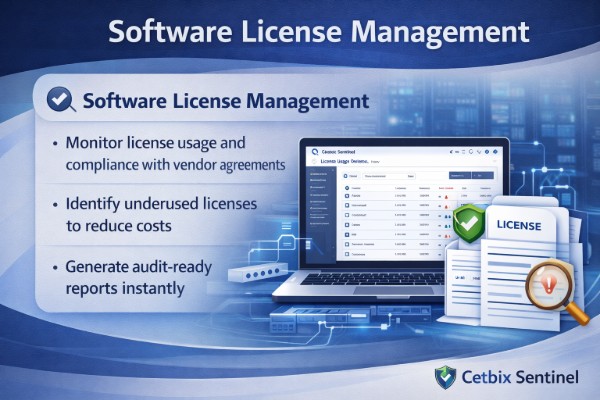
Software Asset Management requires more than knowing which applications are installed.
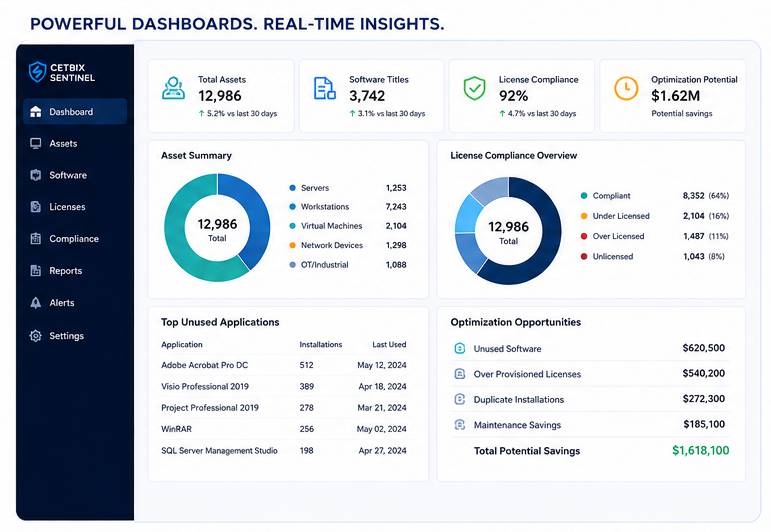
Sentinel connects software discovery with license and entitlement information to help organizations understand their licensing position.
Monitor and analyze:
- License entitlements
- Installed software
- License allocations
- Software utilization
- Subscription licenses
- Perpetual licenses
- Enterprise agreements
- Renewal dates
- Expiration dates
- Potential over-deployment
- Underutilized licenses
- Unused software
Software Installed ≠ Software Needed ≠ Software Licensed
Sentinel helps organizations understand the difference.
Software License Reconciliation
Managing software licenses
06 — Automated License Reconciliation
Identify Potential Compliance Exposure and Optimization Opportunities
Manual license reconciliation can require significant effort and often depends on incomplete inventory information.
Cetbix Sentinel helps connect:
Entitlements → Installations → Assets → Usage
This enables teams to investigate potential:
- Under-licensed deployments
- Over-provisioned licenses
- Unused licenses
- Underutilized software
- License allocation issues
- Renewal requirements
- Software compliance exposure
- Cost optimization opportunities
The result is a more informed approach to software governance and vendor management.
Compliance & Audit Readiness
07 — Vulnerability Intelligence
Know Which Software Is Vulnerable
Software inventory becomes significantly more valuable when it can be connected to vulnerability intelligence.
Sentinel correlates relevant software and versions with vulnerability information such as:
- CVE identifiers
- CVSS scores
- Severity
- Affected products
- Affected versions
- Vulnerability descriptions
- Exploitation prerequisites
- Potential impact
- Available remediation
- Secure software versions
Instead of asking:
“Which CVEs exist?”
Security teams can ask:
“Which relevant vulnerabilities affect software actually present in our environment?”
Exploitation - Attack Behavior
Technology Spending
08 — Exploitation Intelligence
Know What Attackers Are Exploiting
Not every vulnerability represents the same level of practical risk.
Sentinel adds exploitation context to vulnerability intelligence, including CISA Known Exploited Vulnerabilities (KEV) information where applicable.
Teams can identify:
- Known exploited vulnerabilities
- CISA KEV status
- KEV dates
- Required remediation timelines
- Ransomware-associated vulnerabilities
- Recently exploited vulnerabilities
- Affected vendors
- Affected products
The key distinction is between:
Global Exploitation Intelligence
and
Exploitation Affecting Your Environment
This helps security teams focus on vulnerabilities that are both exploited and relevant.
Know & Understand Vulnerabilities Attackers Are Exploiting
09 — MITRE ATT&CK Intelligence
Understand Vulnerabilities in the Context of Attack Behavior
A vulnerability score describes technical severity. It does not always explain how the weakness may matter during an attack.
Sentinel adds MITRE ATT&CK context where relevant to help security teams understand relationships between vulnerabilities, technologies, and adversary behavior.
Teams can investigate relevant:
- Tactics
- Techniques
- Initial access
- Execution
- Privilege escalation
- Credential access
- Persistence
- Lateral movement
- Defense evasion
- Potential attacker objectives
This adds an additional layer of context between:
Vulnerability → Exploitation → Attacker Behavior
AI Software Advisory - Built for IT & OT Environments
Reporting & Data Export
10 — AI Software Advisory
Turn Technical Findings Into Understandable Recommendations
Security and IT teams often have the information they need—but not necessarily the time to manually connect all of it.
Cetbix Sentinel's AI-assisted advisory capabilities help organize relevant technical context around affected software.
For a vulnerability, teams can review information such as:
- Affected software
- Installed version
- Secure version
- CVE
- CVSS
- Vulnerability impact
- Exploitation status
- Risk context
- Upgrade recommendations
- Remediation considerations
From technical finding to practical decision.
Combination of traditional IT systems and operational technology assets
11 — Risk-Based Prioritization
Know What to Fix First
A vulnerability's CVSS score is an important signal—but it should not be the only signal.
Cetbix Sentinel can bring together multiple risk indicators, including:
- CVSS severity
- CISA KEV status
- Exploitation intelligence
- Ransomware association
- Installed software version
- Number of affected assets
- Exposure
- Exploitation prerequisites
- MITRE ATT&CK context
- Available patches
- Recommended secure versions
- Environmental relevance
- Operational considerations
This helps teams move from:
Thousands of findings
to:
A prioritized remediation workload.
12 - AI-Guided Remediation
Move From Detection to Action
Identifying a vulnerability is only the beginning.
Sentinel helps structure the remediation process around the affected asset and software.
Discover
Identify affected systems and software installations.
Validate
Confirm versions, vulnerability conditions, and relevant security information.
Assess
Evaluate severity, exploitation, exposure, and organizational relevance.
Recommend
Identify an appropriate secure version or remediation path.
Test
Validate the remediation on representative systems.
Deploy
Implement the approved update or remediation through the organization's operational processes.
Verify
Rescan and confirm that the vulnerable condition has been addressed.
Investigate
Where exploitation is known or suspected, investigate relevant security and operational telemetry.
Detect → Prioritize → Remediate → Verify
13 - Compliance & Audit Intelligence
Build a Defensible Technology Record
Compliance and audit teams need reliable information about what exists, what is installed, what is licensed, and what has been remediated.
Sentinel helps centralize information across:
- Assets
- Software
- Versions
- Licenses
- Vulnerabilities
- Remediation
- Compliance status
- Reporting
Organizations can use this information to support:
- Software audits
- License compliance reviews
- Internal audits
- Security governance
- Policy enforcement
- Remediation tracking
- Audit preparation
Better visibility creates better evidence.
14 - API, Data Export & Integration
Make Sentinel Part of Your Technology Ecosystem
Asset intelligence becomes more valuable when it can be connected with other operational systems.
Cetbix Sentinel supports capabilities for:
- Structured data export
- API-based integration
- Reporting workflows
- Asset management processes
- Security workflows
- Business intelligence
- Third-party systems
Organizations can use Sentinel data as part of broader ITAM, SAM, security, compliance, procurement, and operational workflows.