Experts in innovation strategies
Downloads Contact
English

Cetbix Sentinel

One Platform for Asset Intelligence, Software Governance & Cyber Risk

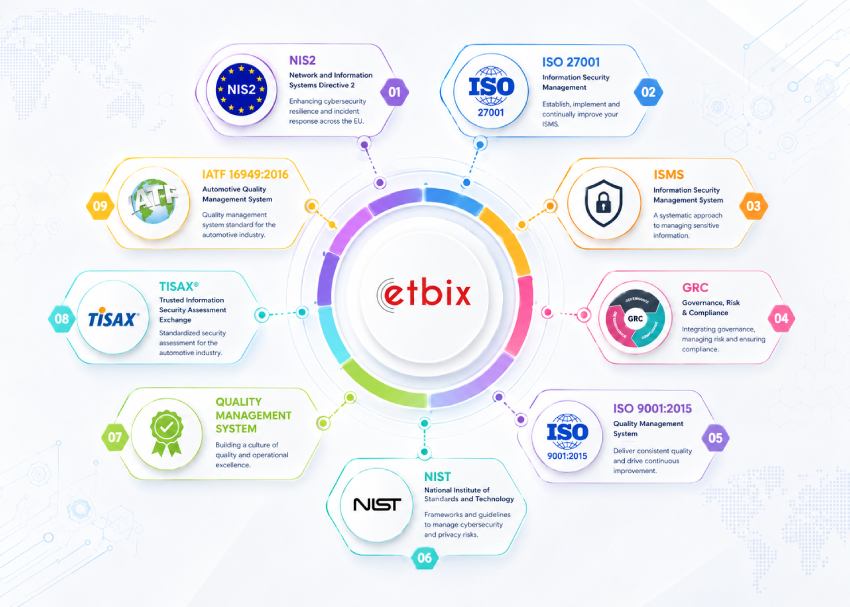
Cetbix supports multi-framework compliance and provides end-to-end traceability across assets, risks, controls, and audit evidence, making it particularly suitable for organizations implementing structured management systems.

Cetbix GRC Platform

One Platform for Asset Intelligence, Software Governance & Risk-Based Vulnerability Management - Supports Windows, Linux and Mac OS

Discover every asset. Govern every licence. Understand cyber risk. Connect vulnerabilities to attack techniques. Prioritise what matters. Remediate with confidence.

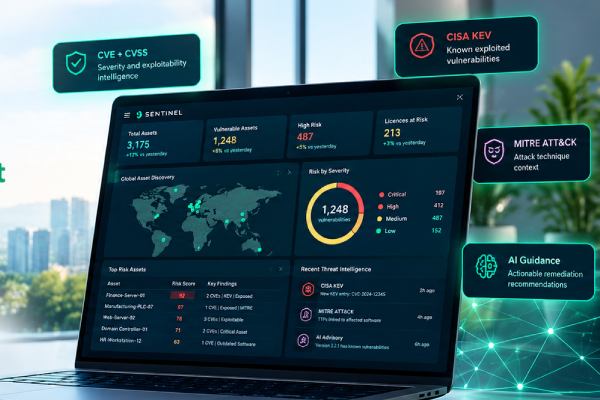
Cetbix Sentinel unifies IT, OT and cloud asset discovery, software asset management, licence governance, risk-based vulnerability management, vulnerability intelligence, CISA Known Exploited Vulnerabilities (KEV), MITRE ATT&CK context and AI-assisted remediation guidance in one centralised platform.

Supporting Windows, Linux and macOS environments, Sentinel connects asset and software inventory with vulnerability severity, exploitability, asset exposure and business criticality to help organisations understand where their greatest cybersecurity risks lie.

By combining CVE/CVSS intelligence, known exploitation data and MITRE ATT&CK techniques with business and operational context, Sentinel helps IT and security teams move beyond vulnerability lists to make informed, risk-based remediation decisions.

From discovering assets and governing software licences to understanding potential attack scenarios and prioritising remediation, Sentinel delivers a clearer, more actionable view of your technology estate and its associated cyber risk.

Know your assets. Understand your risk. Act on what matters.

Know what you have. Know what's vulnerable. Know what's being exploited. Understand how attackers operate. Know what to fix first.

Request a Demo


Testimonials

“Cetbix Sentinel transformed our IT/OT governance — now we have full visibility and compliance without manual tracking.”
— IT Director, Enterprise Company


product

Key Feature

IT/OT/Cloud Asset Discovery & Inventory

🔍 IT/OT/Cloud Asset Discovery & Inventory

  • Automatically discover hardware, software, virtual machines, cloud resources, and connected assets
  • Maintain a centralized, continuously updated technology inventory
  • Identify unmanaged and unauthorized assets
  • Track installed applications and software versions
  • Track assets throughout their lifecycle, from procurement and deployment to retirement
  • Map software and vulnerabilities to affected endpoints and infrastructure

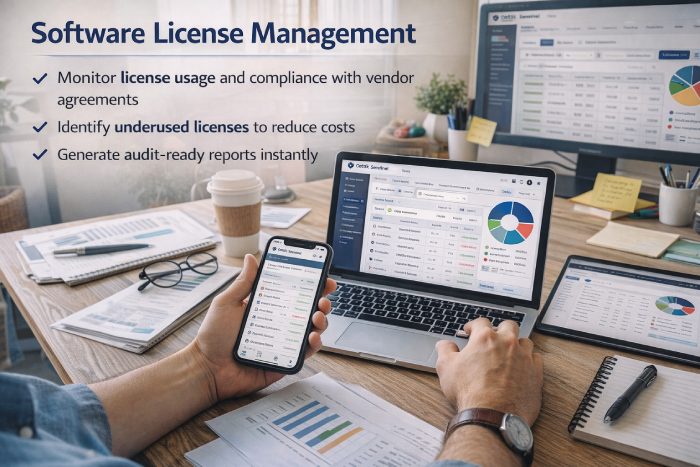
📄 Software License Management

  • Monitor software licenses, entitlements, installations, usage, and renewals
  • Track license start dates, renewal dates, and expiration dates
  • Identify unused and underutilized licenses
  • Detect over-deployment and potential licensing compliance issues
  • Optimize software spending and license allocation
  • Generate audit-ready software and licensing reports
  • Maintain centralized visibility across perpetual, subscription, SaaS, and enterprise licensing models

🛡️ Vulnerability Intelligence & Risk Management

Cetbix Sentinel goes beyond traditional asset inventory by continuously evaluating discovered software against known security vulnerabilities.

The platform correlates installed software versions with CVE intelligence, CVSS severity, exploitation status, affected products, and available remediation information, helping security and IT teams understand which vulnerabilities actually matter to their environment.

Key capabilities

  • Continuously correlate installed software with known CVEs
  • Identify vulnerable and outdated software versions
  • Display CVE identifiers and CVSS risk scores
  • Classify vulnerabilities by severity and business risk
  • Identify assets and software affected by known vulnerabilities
  • Prioritize vulnerabilities affecting your actual technology stack
  • Track remediation status across affected systems
  • Surface newly disclosed and newly exploited vulnerabilities
  • Help security teams distinguish general vulnerability noise from vulnerabilities relevant to their infrastructure
product
product

AI Exploited Vulnerability Intelligence

🚨 CISA KEV & Actively Exploited Vulnerability Intelligence

Cetbix Sentinel integrates CISA Known Exploited Vulnerabilities (KEV) intelligence directly into the platform, giving security teams centralized visibility into vulnerabilities known to be exploited in the wild.

The Exploited Vulnerabilities Catalog provides immediate visibility into:

  • Active exploited CVEs
  • Vulnerability vendor and affected product
  • Vulnerability description
  • Date added to the exploited-vulnerability catalog
  • Remediation due dates
  • Ransomware associations
  • Recently added exploited vulnerabilities
  • Affected vendors
  • Vulnerabilities affecting the organization's own technology stack

Infrastructure-aware filtering

Instead of treating every exploited vulnerability as equally relevant, Sentinel can correlate vulnerability intelligence with the organization's discovered infrastructure.

Teams can quickly distinguish between:

All Known Exploited Vulnerabilities and Known Exploited Vulnerabilities Affecting Our Stack.

This helps security teams concentrate remediation efforts on vulnerabilities that have direct relevance to their environment.


🤖 AI Software Advisory & Version Recommendation

Cetbix Sentinel's AI Software Advisory & Version Recommendation capability analyzes vulnerable software and provides contextual remediation guidance.

For affected applications, Sentinel can present:

  • Currently installed version
  • Recommended secure version
  • Risk score
  • CVSS score
  • CVE identifier
  • Risk assessment
  • Impact analysis
  • Recommended remediation
  • Structured action plan

For example, when Sentinel identifies that an installed application version is affected by a high-risk CVE, its AI analysis can evaluate the vulnerability conditions, explain the potential impact on the affected environment, recommend an appropriate software version, and provide administrators with a practical remediation sequence.

This turns vulnerability information into an actionable remediation workflow rather than another security alert.

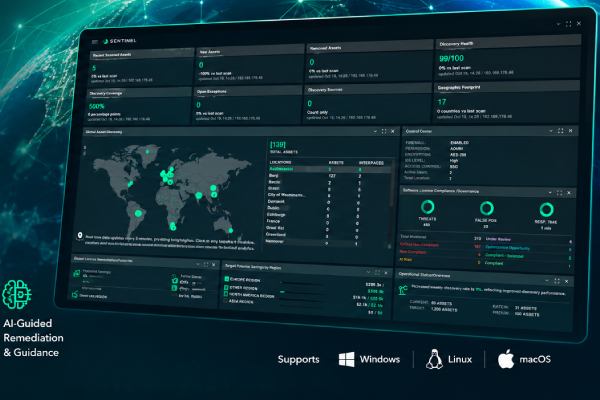
🔧 AI-Guided Remediation

Cetbix Sentinel helps administrators move from detection to remediation.

AI-generated remediation guidance can provide a structured plan covering:

Inventory → Validate → Test → Deploy → Verify

Depending on the vulnerability and software involved, recommendations can include:

  • Identify all affected installations
  • Determine affected operating systems and endpoints
  • Validate whether exploitation prerequisites exist
  • Verify vendor advisories and supported versions
  • Recommend an appropriate secure software version
  • Validate software package authenticity
  • Pilot upgrades on representative systems
  • Deploy through approved endpoint-management processes
  • Rescan assets after remediation
  • Confirm vulnerable versions have been removed
  • Review endpoint and application logs for suspicious activity

This provides IT and security teams with both the technical vulnerability information and the operational steps required to address it.


Risk-Based, Compliance & Governance, Analytics & Security Insights

🎯 Risk-Based Vulnerability Prioritization

Not every vulnerability represents the same level of risk.

Cetbix Sentinel combines multiple signals to help organizations prioritize remediation, including:

  • CVSS severity
  • Known exploitation
  • CISA KEV status
  • Ransomware association
  • Installed software version
  • Presence within the organization's infrastructure
  • Vulnerability prerequisites
  • Software exposure
  • Available remediation
  • Recommended secure versions
  • Business and operational context

This enables teams to focus first on vulnerabilities that present the greatest practical risk to their environment.


⚖️ Compliance & Governance

  • Enforce IT and software policies organization-wide
  • Detect unauthorized and non-compliant software
  • Monitor endpoint software compliance
  • Maintain audit trails for assets, licenses, vulnerabilities, and remediation
  • Track remediation progress
  • Generate compliance and audit-ready reports
  • Improve governance across IT, OT, cloud, and software environments

📊 Analytics & Security Insights

Cetbix Sentinel provides interactive dashboards covering:

  • Asset inventory and utilization
  • Software installations
  • Software license utilization
  • License expiration and renewal
  • Software compliance
  • Vulnerability exposure
  • CVE severity
  • Known exploited vulnerabilities
  • Ransomware-linked vulnerabilities
  • Recently disclosed and exploited vulnerabilities
  • Vendors affected by vulnerabilities
  • Vulnerabilities affecting your infrastructure
  • Remediation progress and outstanding risks

Executive and operational dashboards provide different levels of visibility, allowing technical teams to investigate individual CVEs while leadership monitors overall organizational exposure and remediation progress.

product
product

CISA KEV & Actively Exploited Vulnerability Intelligence

Cetbix Sentinel integrates CISA Known Exploited Vulnerabilities (KEV) intelligence directly into the platform, giving security teams centralized visibility into vulnerabilities known to be exploited in the wild.

The Exploited Vulnerabilities Catalog provides immediate visibility into:

  • Active exploited CVEs
  • Vulnerability vendor and affected product
  • Vulnerability description
  • Date added to the exploited-vulnerability catalog
  • Remediation due dates
  • Ransomware associations
  • Recently added exploited vulnerabilities
  • Affected vendors
  • Vulnerabilities affecting the organization's own technology stack

Infrastructure-aware filtering

Instead of treating every exploited vulnerability as equally relevant, Sentinel can correlate vulnerability intelligence with the organization's discovered infrastructure.

Teams can quickly distinguish between:

All Known Exploited Vulnerabilities and Known Exploited Vulnerabilities Affecting Our Stack.

This helps security teams concentrate remediation efforts on vulnerabilities that have direct relevance to their environment.

🎯 Risk-Based Vulnerability Prioritization

Not every vulnerability represents the same level of risk.

Cetbix Sentinel combines multiple signals to help organizations prioritize remediation, including:

  • CVSS severity
  • Known exploitation
  • CISA KEV status
  • Ransomware association
  • Installed software version
  • Presence within the organization's infrastructure
  • Vulnerability prerequisites
  • Software exposure
  • Available remediation
  • Recommended secure versions
  • Business and operational context

This enables teams to focus first on vulnerabilities that present the greatest practical risk to their environment.


AI Software Advisory & Version Recommendation

Cetbix Sentinel's AI Software Advisory & Version Recommendation capability analyzes vulnerable software and provides contextual remediation guidance.

For affected applications, Sentinel can present:

  • Currently installed version
  • Recommended secure version
  • Risk score
  • CVSS score
  • CVE identifier
  • Risk assessment
  • Impact analysis
  • Recommended remediation
  • Structured action plan

For example, when Sentinel identifies that an installed application version is affected by a high-risk CVE, its AI analysis can evaluate the vulnerability conditions, explain the potential impact on the affected environment, recommend an appropriate software version, and provide administrators with a practical remediation sequence.

This turns vulnerability information into an actionable remediation workflow rather than another security alert.


product
product

Centralized Asset & Security Intelligence

🛠️ Cetbix Sentinel creates a unified relationship between:

Asset → Operating System → Installed Software → Software Version → License → CVE → Exploitation Intelligence → Risk → Recommended Version → Remediation

Instead of maintaining separate inventories for asset management, licensing, compliance, and vulnerability management, organizations gain a consolidated technology intelligence platform.

Role-based access provides appropriate visibility for:

IT Operations • Security • OT • Cloud • Finance • Compliance • Management


Optional AI & Intelligence Modules

Sentinel Discover

Advanced asset discovery, endpoint inventory, software discovery, and infrastructure visibility.

Sentinel License

Software entitlement, utilization, renewal, compliance, and cost optimization.

Sentinel Vulnerability Intelligence

CVE correlation, CVSS analysis, CISA KEV intelligence, ransomware associations, exploited vulnerability tracking, and infrastructure-aware vulnerability prioritization.

Sentinel AI Advisory

AI-powered software risk assessments, impact analysis, secure-version recommendations, and structured remediation plans.

Sentinel Insights

Executive analytics, technology risk intelligence, predictive reporting, compliance trends, and optimization insights.

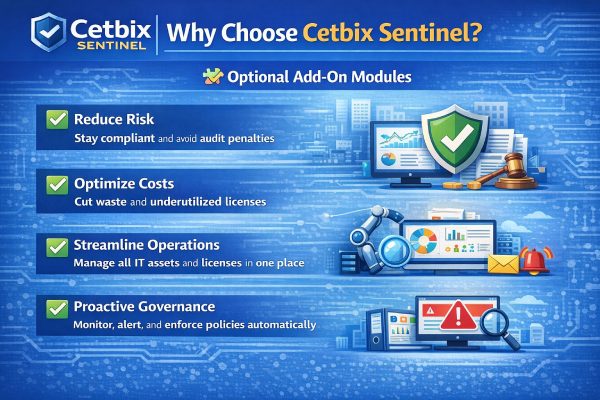
Why Choose Cetbix Sentinel?

  • ✅ Know What You Have — Continuously discover IT, OT, cloud assets and installed software.
  • 🛡️ Know What Is Vulnerable — Correlate software and versions with CVEs and security intelligence.
  • 🚨 Know What Is Being Exploited — Monitor CISA KEV and actively exploited vulnerabilities.
  • 🎯 Know What Affects You — Prioritize vulnerabilities against your actual infrastructure instead of treating every CVE equally.
  • 🤖 Know What To Do Next — Receive AI-generated risk assessments, impact analysis, secure-version recommendations, and remediation plans.
  • 🔄 Verify Remediation — Rescan environments to confirm vulnerable software has been upgraded or removed.
  • 💰 Optimize Software Spend — Identify unused and underutilized licenses.
  • ⚖️ Strengthen Compliance — Combine asset, licensing, vulnerability, and remediation evidence for audit readiness.
  • 📊 Give Executives Visibility — Translate technical asset and vulnerability information into business-level risk intelligence.
product
product

Cetbix Sentinel - Frequently Asked Questions (FAQs)

Cetbix Sentinel FAQs

Platform Overview

1. What is Cetbix Sentinel?

Cetbix Sentinel is a unified Risk-Based Vulnerability Management (RBVM), IT/OT/cloud asset intelligence and software governance platform. It combines agentless discovery, software inventory, vulnerability intelligence, CISA KEV, MITRE ATT&CK context and AI-assisted remediation guidance.

2. What makes Cetbix Sentinel different from traditional vulnerability management tools?

Sentinel connects vulnerability findings with software inventory, asset exposure, business criticality, exploitability and attack context. It also provides software licence governance, helping teams manage cybersecurity risk and software expenditure together.

3. Is Cetbix Sentinel a Risk-Based Vulnerability Management (RBVM) solution?

Yes. Sentinel evaluates vulnerabilities in the context of technical severity, exploitability, exposure, known exploitation and business criticality to help teams focus on the most consequential risks.

4. Which operating systems does Cetbix Sentinel support?

Sentinel supports Windows, Linux and macOS environments. The depth of discovery and available information can vary by operating system, integration and deployment configuration.

5. Who should use Cetbix Sentinel?

Sentinel is designed for cybersecurity teams, vulnerability managers, IT administrators, software asset managers, compliance teams and technology leaders responsible for complex IT and OT environments.

Asset Discovery and Inventory

6. How does Cetbix Sentinel discover IT and OT assets?

Sentinel uses agentless discovery and supported infrastructure data sources to identify assets, operating systems, installed software and relevant system information across applicable IT, OT and cloud environments.

7. Does Cetbix Sentinel require endpoint agents?

Sentinel is designed around agentless discovery. Depending on the environment, it uses supported network discovery methods, integrations and available management data sources without requiring a dedicated Sentinel agent on every asset.

8. Can Cetbix Sentinel identify unmanaged or unknown assets?

Yes. Discovery and inventory comparisons help reveal newly detected assets, assets absent from existing records and changes that require investigation.

9. Does Cetbix Sentinel support cloud and hybrid environments?

Yes. Sentinel supports applicable on-premises, cloud and hybrid asset intelligence. Visibility depends on configured discovery sources, permissions and supported integrations.

10. What asset information does Cetbix Sentinel collect?

Depending on the source, Sentinel can capture device identifiers, operating systems and versions, installed software, running processes and services, network and location information, software usage and discovery status.

11. Does Cetbix Sentinel provide geographic asset visibility?

Yes. Geographic dashboards help teams view the distribution of discovered assets and related inventory information across locations.

12. Can Cetbix Sentinel track changes in the asset inventory?

Yes. Sentinel highlights newly discovered and removed assets, recent discovery activity and inventory changes to support ongoing asset visibility.

Risk-Based Vulnerability Management

13. How does Cetbix Sentinel identify software vulnerabilities?

Sentinel correlates discovered software and version information with known vulnerability intelligence, including CVE records and CVSS severity data, to flag software that may be affected.

14. Does Cetbix Sentinel use CVE and CVSS information?

Yes. CVE identifiers and CVSS scores provide technical vulnerability context that Sentinel enriches with exposure, exploitability, exploitation activity and business impact.

15. How does Cetbix Sentinel prioritise vulnerabilities?

Sentinel considers vulnerability severity, exploitability, known exploitation, asset exposure, business criticality and relevant threat context to help prioritise remediation.

16. Does Cetbix Sentinel assess business criticality?

Yes. Sentinel includes business criticality as a structured input so that the importance of affected assets influences remediation priority.

17. Does Cetbix Sentinel assess asset exposure?

Yes. Sentinel incorporates asset exposure into contextual risk assessment to distinguish vulnerabilities affecting more exposed assets.

18. Does Cetbix Sentinel evaluate exploitability?

Yes. Exploitability intelligence is part of Sentinel’s structured risk assessment and helps teams interpret how likely or practical exploitation may be.

19. Does Cetbix Sentinel integrate CISA Known Exploited Vulnerabilities (KEV)?

Yes. Sentinel incorporates the CISA Known Exploited Vulnerabilities (KEV) Catalog to identify vulnerabilities with documented exploitation in the wild.

20. How does CISA KEV improve vulnerability prioritisation?

KEV data identifies vulnerabilities known to have been exploited. Sentinel combines this evidence with exposure, business criticality, exploitability and severity to support remediation decisions.

21. Does Cetbix Sentinel support MITRE ATT&CK?

Yes. Sentinel incorporates MITRE ATT&CK context to help teams understand relevant adversary tactics and techniques associated with security risks.

22. How does MITRE ATT&CK improve risk assessment?

MITRE ATT&CK provides a structured view of adversary behaviour. Sentinel uses relevant technique context to help teams interpret potential attack scenarios and plan remediation.

23. Does Cetbix Sentinel provide ransomware-related intelligence?

Yes. Sentinel incorporates ransomware-related threat context to help teams evaluate relevant vulnerabilities alongside exploitation evidence and asset risk.

24. Can Cetbix Sentinel identify outdated or unsupported software?

Yes. Its software inventory and version intelligence help identify outdated applications and versions that warrant updating, replacement or further review.

25. Does Cetbix Sentinel perform active vulnerability scanning?

Sentinel’s core vulnerability intelligence correlates discovered assets and software versions with known vulnerability data. This is different from intrusive active vulnerability scanning or penetration testing; confirm any additional scanning capabilities for your deployment.

AI-Assisted Remediation and Risk Intelligence

26. What AI capabilities does Cetbix Sentinel provide?

Sentinel provides AI-assisted software advisory and remediation guidance to help teams interpret findings, understand risk and identify potential corrective actions.

27. Does Cetbix Sentinel recommend vulnerability remediation actions?

Yes. Sentinel provides guidance such as reviewing affected software, assessing available updates and addressing high-priority findings. IT and security teams retain responsibility for validating and implementing changes.

28. Can Cetbix Sentinel automatically prioritise remediation?

Sentinel supports risk-based prioritisation by combining vulnerability intelligence with exploitability, exposure, known exploitation and business criticality.

29. How does Cetbix Sentinel help reduce cyber risk?

It improves asset visibility, highlights potentially vulnerable software, identifies known exploitation context and directs attention to the most significant remediation priorities.

30. Does Cetbix Sentinel provide actionable security intelligence?

Yes. Sentinel brings together asset, software, vulnerability, exploitation and MITRE ATT&CK context to help turn technical findings into informed remediation decisions.

Software Asset Management and Licence Governance

31. Does Cetbix Sentinel include Software Asset Management (SAM)?

Yes. Sentinel supports software inventory, usage analysis, licence governance, compliance assessment and software optimisation.

32. How does Cetbix Sentinel manage software licence compliance?

Sentinel helps reconcile software installations and usage with available licence entitlement records, highlighting potential compliance gaps and discrepancies.

33. Can Cetbix Sentinel identify unused or underutilised software licences?

Yes. Available software usage and entitlement information can reveal unused or underutilised licences that may be candidates for reclamation or optimisation.

34. Does Cetbix Sentinel track licence expiration and renewals?

Yes. Sentinel provides visibility into recorded licence expiration and renewal dates so teams can identify upcoming actions.

35. Can Cetbix Sentinel help reduce software licensing costs?

Yes. Licence reconciliation, software usage analysis and optimisation reporting can reveal potential savings and unnecessary expenditure.

36. Does Cetbix Sentinel provide software vendor expenditure reporting?

Yes. Sentinel provides vendor spend and software cost insights to support budgeting and optimisation.

37. Can Cetbix Sentinel identify software compliance and optimisation issues?

Yes. Sentinel highlights licence discrepancies, renewal concerns, underused entitlements and other software governance issues that warrant review.

Dashboards, Reporting and Operations

38. What dashboards are available in Cetbix Sentinel?

Depending on edition and configuration, dashboards cover discovery health, asset coverage and geography, hardware and software inventory, licence reconciliation, potential savings, vendor expenditure, renewals, vulnerability intelligence and risk priorities.

39. Does Cetbix Sentinel provide executive reporting?

Yes. Consolidated dashboards and reports help communicate asset visibility, licence governance, expenditure, compliance and cybersecurity risk to decision-makers.

40. Can Cetbix Sentinel track discovery and compliance trends?

Yes. Sentinel helps monitor discovery coverage, inventory changes, software compliance and related trends over time.

41. Does Cetbix Sentinel help identify assets requiring immediate attention?

Yes. Sentinel highlights assets affected by elevated vulnerability risk, known exploitation, exposure, business criticality or software governance concerns.

42. Does Cetbix Sentinel support continuous monitoring?

Sentinel supports ongoing discovery, inventory refreshes and monitoring of relevant software and governance data. Frequency depends on configuration, source availability and integrations.

Integration, Security and Deployment

43. Can Cetbix Sentinel integrate with existing enterprise tools?

Sentinel provides API and integration capabilities for connecting supported asset, infrastructure and security data sources. Specific connectors and scope should be confirmed for the deployment.

44. Can Cetbix Sentinel work alongside existing ITSM, CMDB or SIEM tools?

Yes. Sentinel can complement these systems with asset intelligence, software governance and contextual vulnerability information. It is not positioned as a replacement for a complete ITSM or SIEM platform.

45. How does Cetbix Sentinel protect operational information?

Sentinel offers enterprise security and access-control capabilities. Specific encryption, authentication, audit, hosting and data protection controls should be verified for the selected edition and deployment.

46. How long does Cetbix Sentinel take to deploy?

Deployment depends on asset volume, network complexity, permissions, discovery methods and integrations. Initial discovery can begin after the required connectivity and configuration are established.

47. Is Cetbix Sentinel suitable for large enterprises?

Yes. Sentinel is intended for organisations with distributed assets and centralised requirements for software governance, asset intelligence and risk-based vulnerability management. Enterprise sizing is tailored to deployment needs.

48. Which industries can benefit from Cetbix Sentinel?

Manufacturing, healthcare, financial services, education, government, retail, logistics, technology and other sectors with significant IT or OT estates can benefit.

Pricing and Getting Started

49. How is Cetbix Sentinel licensed?

Sentinel is offered in annual, asset-based subscription editions: Discover for asset inventory, Govern for software governance, Intelligence for vulnerability and risk intelligence, and Enterprise for tailored large-scale requirements. Confirm current pricing and edition inclusions with Cetbix.

50. How can I get started with Cetbix Sentinel?

Request a demonstration to explore asset discovery, licence governance, vulnerability intelligence, MITRE ATT&CK context and risk-based remediation.